Your VCF network model decides how many firewall rules you open
Same products, same features, same answers. Only the network model changed, and the final rule count moved from 176 to 228. Here is why, and why you should compare models before committing to a design.
Most firewall conversations start after the network design is settled. That is late. The network model you choose has a direct effect on how many rules the firewall team will have to open and maintain.
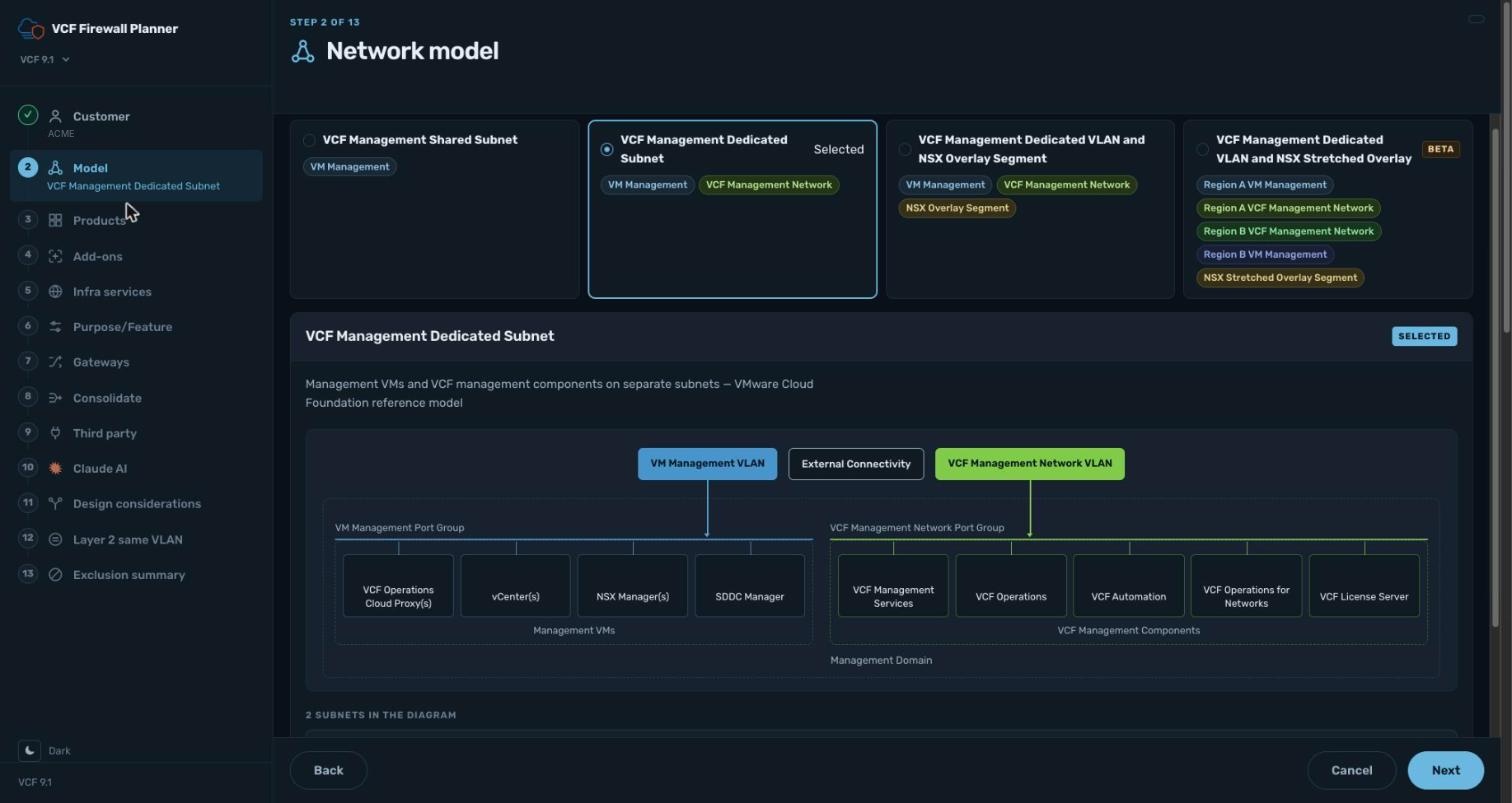
Same selections, different models
We ran the same assessment three times, changing only the network model. Every product, add-on, service, feature and design answer stayed the same.
| Network model | Final rules |
|---|---|
| Model 1: Shared | 176 |
| Model 2: Dedicated (ACME) | 224 |
| Model 3: Overlay | 228 |
The spread is 52 rules, about 30% more on the highest model than on the lowest.
Why the count changes
The difference comes almost entirely from Layer 2. A shared subnet keeps more traffic inside one VLAN, and traffic that stays inside a VLAN never crosses a firewall. Split the same components across dedicated subnets, or place them on overlay segments, and more flows cross a boundary that needs a rule.
What we recommend
- Run the assessment for each candidate model before you lock the design. It takes minutes, because every other answer carries over.
- Bring the numbers to the design review. "Model 2 means 48 more rules than Model 1" is a concrete cost the security team can weigh against the segmentation benefit.
- Keep the exclusion summary for the model you choose. It records why each flow was left out, which is what auditors and reviewers ask for later.
ACME chose Model 2, so it opens 224 rules, with the reasons for every one of the 559 exclusions on file.
Compare models on your own design with the VCF Firewall Planner.